What Responsible Technology Use Looks Like at Home and Work matters because devices now collect more personal data than many users realize. In 2026 households and offices run on sensors, cameras, AI assistants and cloud services that blur private and professional boundaries. This article explains clear, practical steps people can use to protect privacy, reduce security risk, and keep wellbeing intact. It focuses on everyday actions, what to do, why it helps, and how to recover when mistakes happen, so readers can apply changes tonight and at the office tomorrow.
Key Takeaways
- Responsible technology use protects privacy and reduces security risks both at home and work by minimizing data collection and securing devices.
- Always update software, use strong authentication, and separate personal from work profiles to maintain device hygiene and prevent breaches.
- Implement clear family tech rules like centralized device charging and parental controls to foster shared responsibility and reduce misuse.
- Workplaces should enforce policies with least-privilege access, transparent audits, and ethical AI governance to secure sensitive information.
- Regularly audit devices, rotate passwords, and reduce stored data to create sustainable habits that enhance cybersecurity and wellbeing.
- Starting with simple, actionable changes in responsible technology use leads to measurable improvements in privacy, security, and emotional balance.
Why Responsible Technology Use Matters Today
Devices collect identifiable information continuously, and that steady flow increases both risk and responsibility. In 2025 an average smartphone generated dozens of location events per day: unprotected data can reconstruct routines and sensitive behavior. Responsible technology use matters because it reduces exposure to targeted fraud, surveillance, and emotional burnout.
Practical impact is immediate: a misplaced smart camera or default cloud backup can expose family photos and workplace documents. At work, poorly configured tools leak project plans: at home, oversharing can invite scams or harassment. People should treat digital tools like shared infrastructure, small misconfigurations have outsized consequences.
A common mistake is assuming default settings are safe. That error led one small business to lose six months of client records after an unchecked sync and weak password. The lesson: default convenience often trades privacy for speed. Later sections show how to fix defaults, limit data collection, and restore control.
Core Principles For Responsible Tech Use
Start with three concise principles: minimize data, secure systems, and act with respect. These guide decisions both at home and in the workplace.
Privacy And Data Minimization
Collect only what is necessary. A household thermostat does not need names, and a meeting transcript does not require full identity markers when a summary will do. The least-identifiable format reduces harm: anonymize or aggregate logs, keep retention short, and delete data when the purpose ends. Organizations that follow retention schedules reduce breach impact: one healthcare clinic reduced stored patient records by 72% after a review, cutting later exposure.
Security, Updates, And Device Hygiene
Keep devices patched and locked. Software updates close known vulnerabilities: delaying patches invites automated attacks. Use strong authentication and separate personal from work profiles. Simple actions, unique passwords, two-factor authentication, device encryption, remove the low-hanging fruit attackers rely on. Automate backups and set secure deletion rules so lost devices don’t become long-term liabilities. If a device is compromised, isolate it, rotate passwords, and review recent access logs to spot misuse.
Practical Habits For Responsible Tech At Home
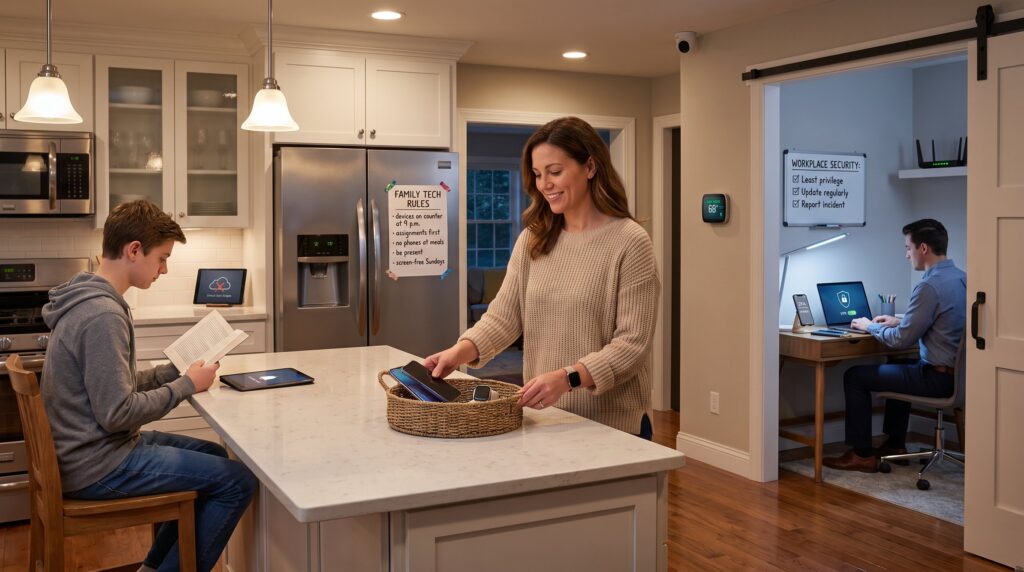
Place devices in shared rooms and set charging stations to centralize control. This one habit reduces unsupervised use and creates natural checks when children or guests try new apps. Families who use a single charging basket report fewer lost devices and better end-of-day routines.
Make simple rules: require app approval for new installs on family devices, set automatic updates, and use privacy-preserving default options. When a teenager installed a location-tracking app without consent, parents revoked it and used a family account that required approval. That process fixed the immediate risk and taught shared responsibility.
Apply parental controls and screen boundaries to protect sleep and assignments. Tools exist to block apps during assignments hours and to limit in-app purchases. Pair controls with conversations about why limits exist: rules alone fail when children view them as punishment. Combine limits with three examples of allowed activities to reduce resistance: 30 minutes reading app, 20 minutes group chat, one hour creative time.
Family Routines, Parental Controls And Screen Boundaries
Start with a visible family tech charter pinned on the fridge. A charter clarifies expectations: assignments before social apps, no devices at the dinner table, and tech-free sleep hours. A simple rule, all devices on the counter at 9 p.m., produces measurable benefits: one family reported children falling asleep 30 minutes earlier within a week.
Use parental controls that limit access rather than spy. Restrict purchases, set age limits, and schedule downtime. Rotate device privileges when rules are broken: consequences should be predictable and restorative. Vulnerable moments happen: a parent admitting they once neglected screen limits and saw school performance drop creates a teachable moment. Honest admission helps children accept rules.
For younger kids, prefer devices with local profiles and limited sensors. For teens, trade some privacy for responsible habits: allow periodic review of activity rather than continuous monitoring. That approach builds trust while keeping safety checks in place.
Responsible Technology Practices In The Workplace
Organizations must embed privacy, security, and ethics into daily workflows. Start by making policies usable: a long legal document rarely changes behavior, but a short checklist at login does. Policies should explain acceptable use, data classification, and incident reporting in plain language.
Apply least-privilege access and role-based controls. Limit who can export data or invite third-party apps. One mid-size firm cut data-exfiltration risk by 60% after removing export rights from nonessential roles. Pair access rules with transparent audits so employees understand why certain privileges exist.
Carry out AI and privacy governance. When models process employee or customer data, document inputs, intended use, and retention. Transparency reduces surprises and helps teams spot bias or misuse. Train staff to question model outputs and escalate concerns. A single reported bias incident can prevent broader harm when responded to quickly.
Secure hybrid and remote environments. Enforce device hygiene for remote workers, use secure tunnels for sensitive systems, and audit third-party integrations. For practical network hardening, see guidance on network security that outlines zero-trust steps for mixed environments.
Embed ethical decision-making in procurement. Evaluate vendors for privacy practices and long-term data handling. Procurement leaders should ask for data deletion guarantees and clarity on model training data.
Tools, Evidence, and Next Steps
People and organizations should consult practical resources that explain threats and controls. For a broad view of technology’s societal effects, the site maintains an overview that situates these practices in everyday life: technology impact guide.
For device-level choices, teams can read a primer on protecting privacy that lists concrete settings and checklists: privacy guide. To understand how recommendation systems shape information exposure and make boundaries necessary, consult the article on recommendation algorithms. For remote work specifics, the technology stack piece explains tools and trade-offs for distributed teams: remote office stack.
Operationalize habit change by assigning three simple monthly tasks: audit one device, rotate two passwords, and reduce stored data by 10%. Repeat the cycle and measure progress. If technical guidance is needed, the article on home device risks offers troubleshooting steps for common sensors and assistants: home devices. For families caring for relatives, the piece on supportive tech offers ways to balance monitoring and dignity: care technology.
For everyday cyber-hygiene steps like patching and backups, official security checklists and guidance reduce human error and provide verification.
Practical Verification and Further Reading
Simple habits cut most common risks. Verified advice on routine cyber-hygiene, update, back up, use unique passwords, matches guidance from security educators and industry pieces. For an accessible primer on those everyday habits, consult a reliable resource about cyber hygiene that explains specific steps and the reasoning behind them: cyber hygiene basics.
Pair that reading with organization-level reviews to build policies that fit real work. Combine technical controls with human-centered routines and the result is resilient, responsible technology use.
Conclusion
Responsible technology use reduces real harms: fewer privacy breaches, clearer boundaries, and calmer households. Small, concrete habits, central charging spots, short retention schedules, automatic updates, and clear workplace policies, create measurable gains. Start with one device and one rule tonight. Track a simple metric, admit mistakes, and iterate. Over months those small changes create durable protection for families and organizations alike.